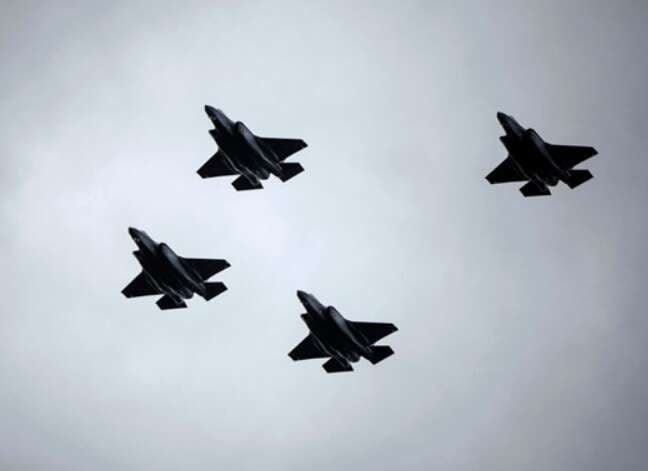
Denmark buys long-range missiles for first time, Moscow warns of consequences
Copenhagen announced a deal to acquire precision-guided missiles to deter aggression. The Russian embassy accused the country of creating a threat.
Copenhagen announced a deal to acquire precision-guided missiles to deter aggression. The Russian embassy accused the country of creating a threat.
Signal developers fixed a serious vulnerability that allowed attackers to access the camera and microphone after a call ended.
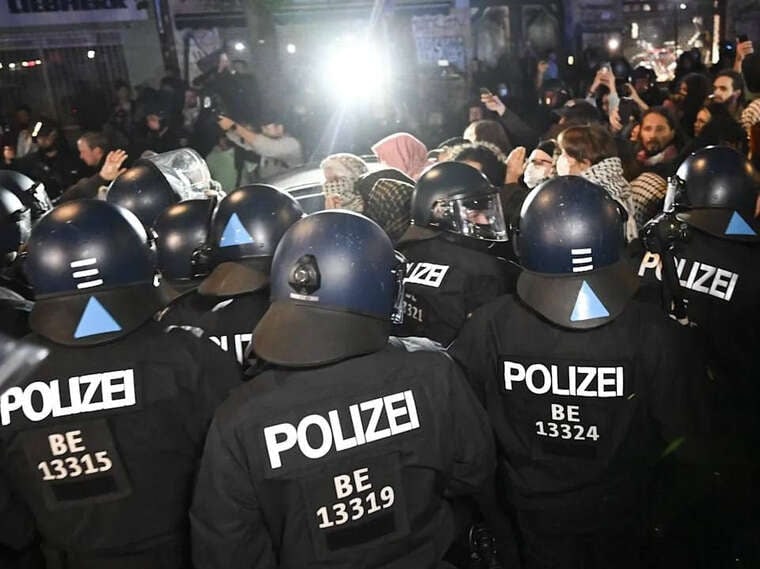
Following the Left Party's victory in the capital, the number of applications from law enforcement officers to transfer to other federal states has increased. Unions warn of a risk of staff shortages.
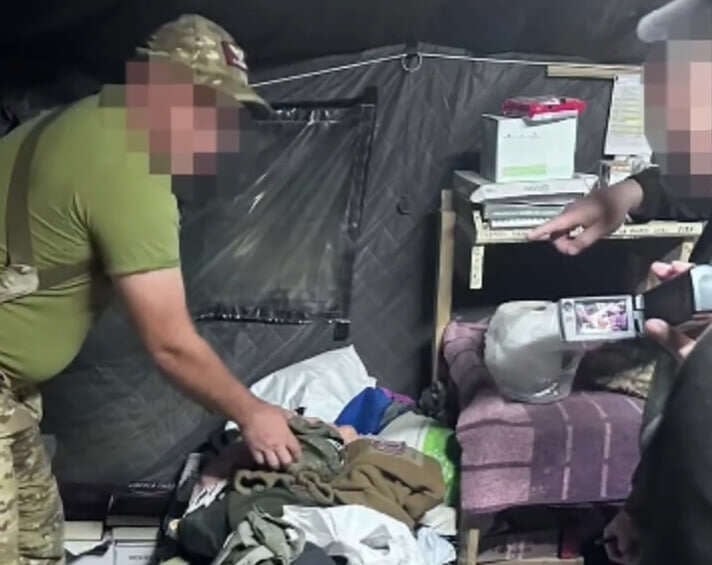
A training company commander demanded $4,000 for permission to leave the unit for a trip to Lviv for his own wedding. After getting married, the serviceman failed to return to duty.
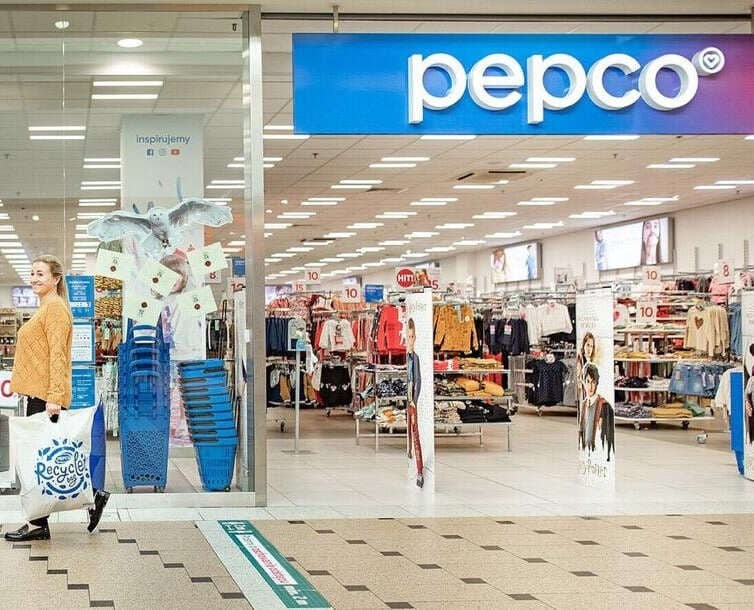
The Polish discounter has launched its first stores in Kyiv. The outlets are located in the Respublika Park, Retroville and Dream Yellow shopping and entertainment centres.
Despite fines and a ban on participating in procurement, affiliated enterprises continue to secure state contracts, replacing coal with a mixture of waste rock and soil.
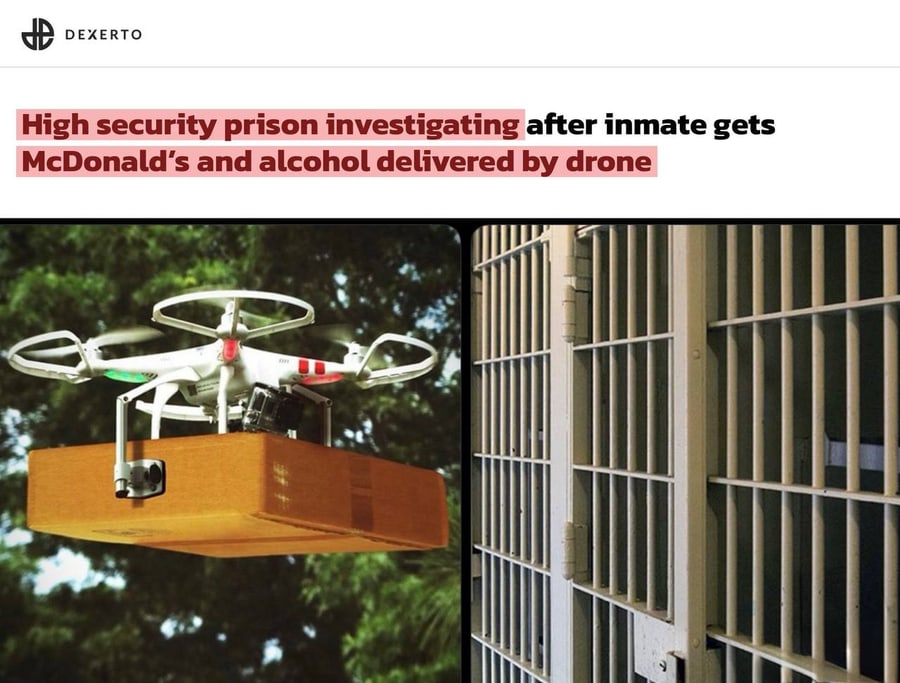
An inmate at a Canadian maximum-security prison received nuggets, fries and alcohol via drone. The administration is conducting an investigation.
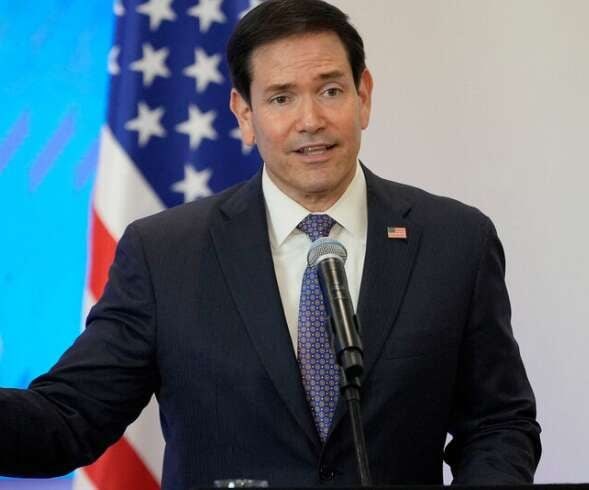
US Secretary of State Marco Rubio explained that the conflict boils down to control over a region comprising 11% of Ukraine's territory, urging both sides to make mutual concessions.
Cybersecurity experts identified a critical vulnerability in the popular messenger Signal. This bug posed a risk of unauthorised access to audio and images from users' cameras. According to expert assessments, the severity level of this flaw was 9.3 out of a maximum possible 10, indicating its high criticality.
As noted, the issue was triggered in a situation where a counterpart intentionally performed an action that caused the application to crash. Such a manipulative process could prevent the command responsible for ending the call from functioning correctly. As a result, the microphone and camera continued transmitting data even after the formal end of the conversation, allowing eavesdropping and image capture.
The Signal development team has already resolved this vulnerability. The fix was implemented in September 2026. However, the public disclosure of incident details occurred later — on 20 October. To date, no confirmed cases have been recorded where this error was used for actual surveillance of users.
To ensure the full security of their data, experts advise updating the Signal messenger to the latest available version, which contains the relevant security patches, as soon as possible.
Comments
No comments yet. Be the first!