Criminals demand $768m to keep Revolut client data undisclosed
Personal and financial data of users, including the owner of Gamdom and Skins.com, may have been leaked following a cyberattack on the British fintech bank.
Personal and financial data of users, including the owner of Gamdom and Skins.com, may have been leaked following a cyberattack on the British fintech bank.
Vitaliy Kovalskyi, current head of a department at the Prosecutor General's Office who previously underwent lustration, is seeking the position of deputy head of the Specialised Anti-Corruption Prosecutor's Office.
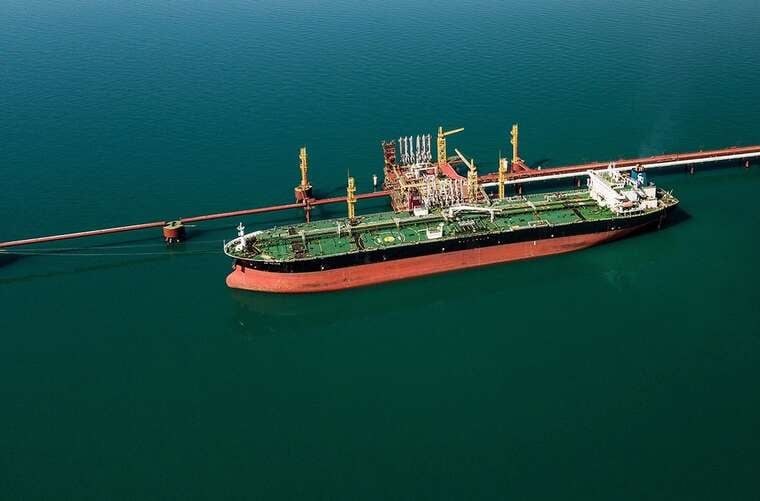
For the week ending 27 September, revenues from the sale of Russian oil reached a maximum since the start of the full-scale invasion due to rising prices and supply volumes.
Larysa Moskviska, who presents herself as a financial planning expert, publishes content for the scandal-hit KIT Group, whose activities were restricted by the National Bank of Ukraine.
The politician died at the age of 61 in a road traffic accident. He served as the director of the "Klass" supermarket chain in Kharkiv.
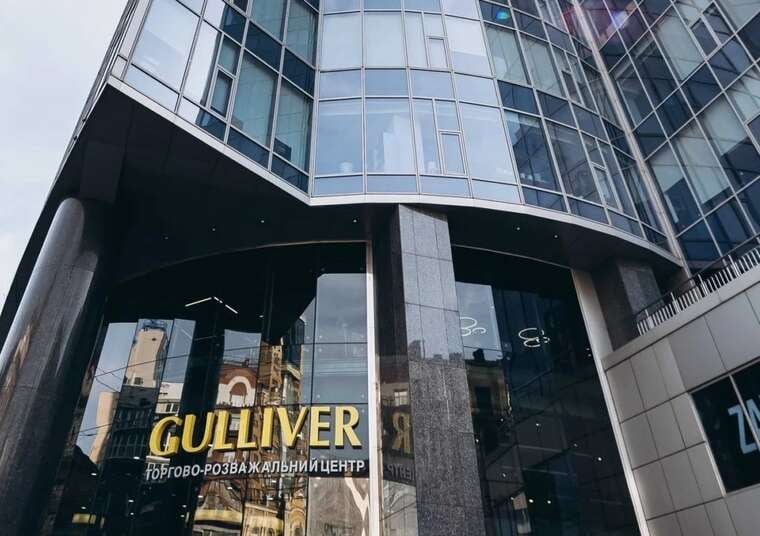
Oschadbank and Ukreximbank have announced a stock exchange auction for the disposal of a large office and retail complex in Kyiv, previously seized due to debts.
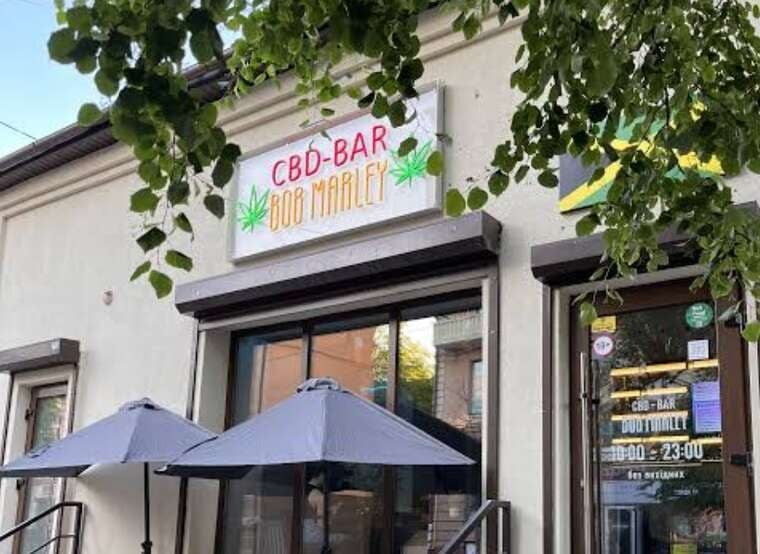
Law enforcement detained 17 individuals who sold vapes containing narcotics through "Bob Marley" venues and online stores, disguising them as legal supplements.
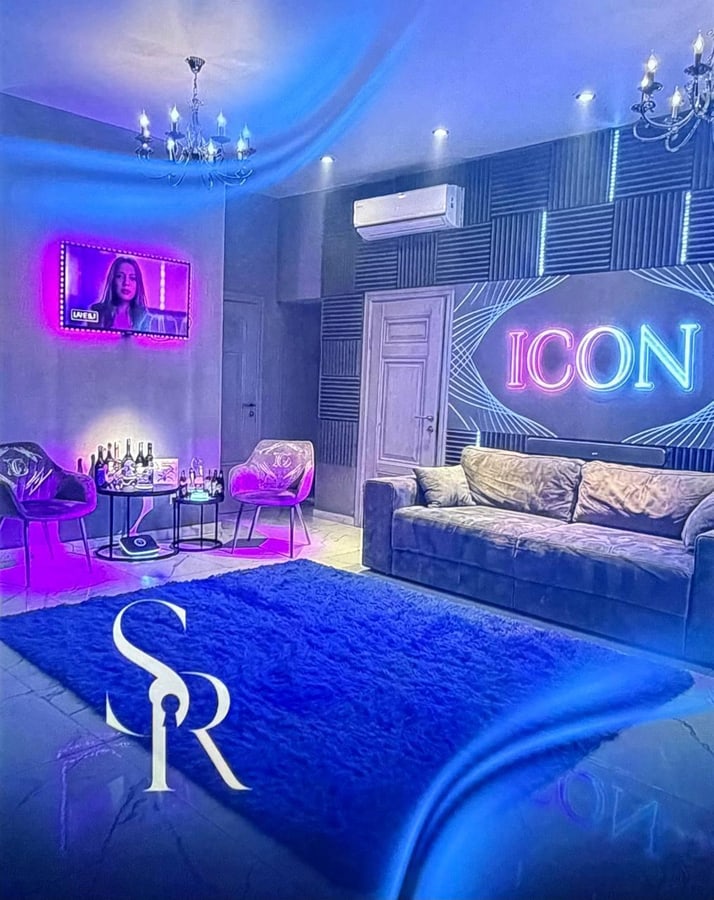
According to the authors of the publication, an establishment providing intimate services may be operating in the Delmar residential complex in central Dnipro. It concerns an apartment on the 15th floor of the building at 72B Dmytro Yavornytskoho Avenue.

Comments
No comments yet. Be the first!