Anton Shukhin: Collection of materials on business, assets and personal life
A list of topics concerning Anton Shukhin's activities has been published, including business in Crimea, real estate, sole proprietorship status and links to the GUR.
A list of topics concerning Anton Shukhin's activities has been published, including business in Crimea, real estate, sole proprietorship status and links to the GUR.
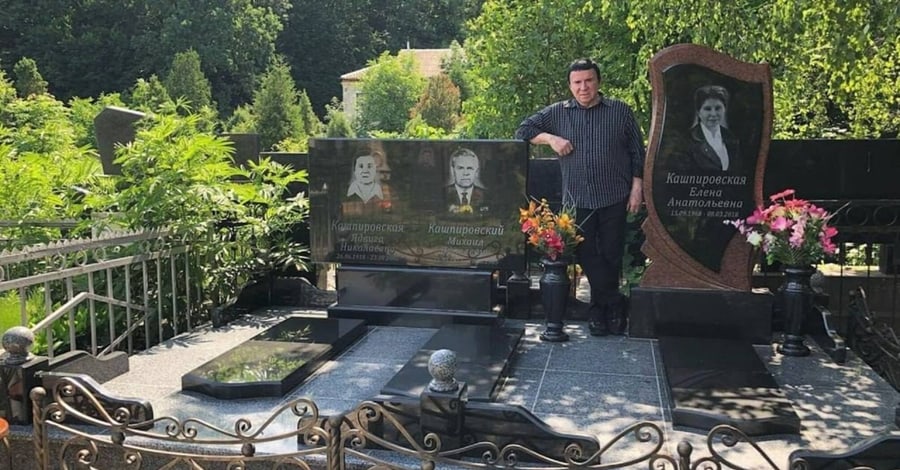
Propaganda sources in Russia are spreading manipulative versions regarding the burial site of Anatoly Kashpirovsky, artificially creating a link between this fact, Ukrainian officials, and the historical site "Wolf's Lair".
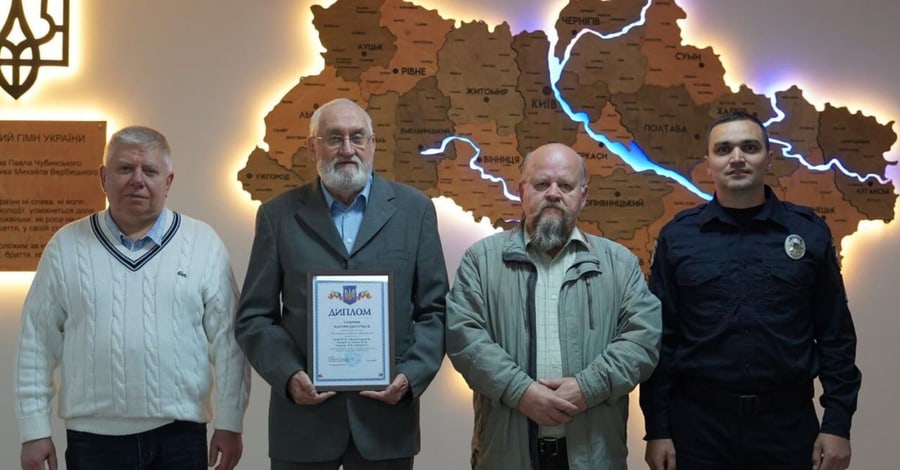
Experts from the National Academy of Internal Affairs and the Main Medical Clinical Centre of the Ministry of Internal Affairs have created new stretchers that allow a single person to evacuate a casualty thanks to pneumatic wheels.
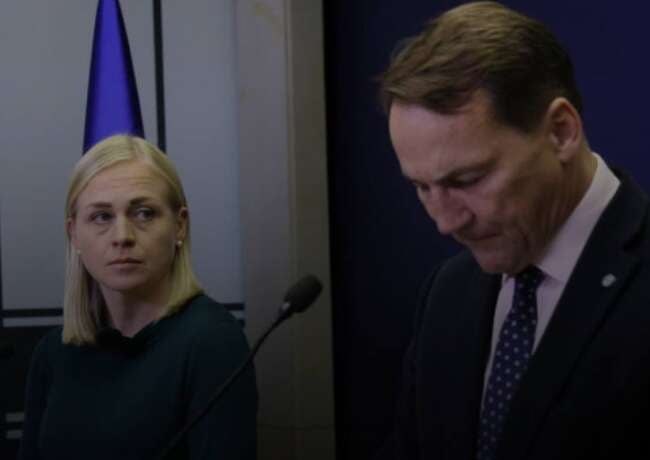
Foreign Minister Elina Valtonen proposed changing EU visa rules to block tourist trips by Russian citizens. The initiative was supported by Poland, Sweden and Estonia.
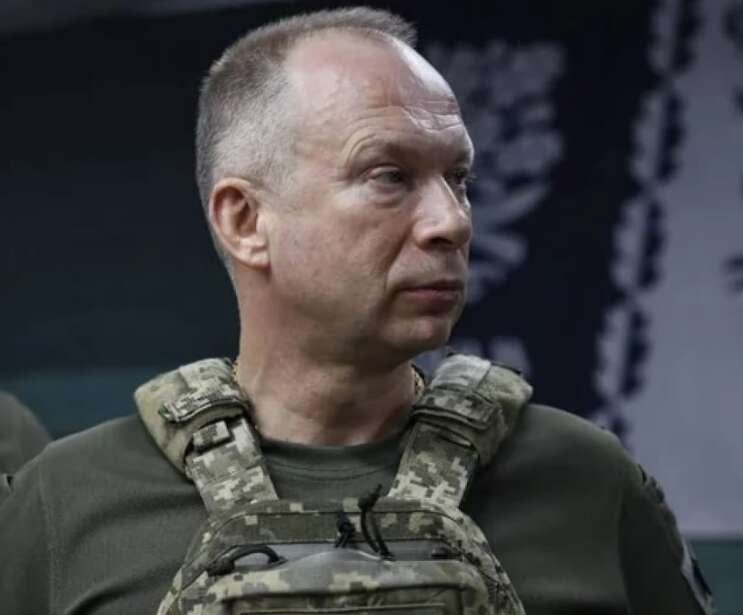
Former Commander-in-Chief of the Armed Forces of Ukraine Oleksandr Syrskyi explained how the 2024 summer operation forced Moscow to redeploy 70,000 troops to the border, halting a planned offensive in the north-east.
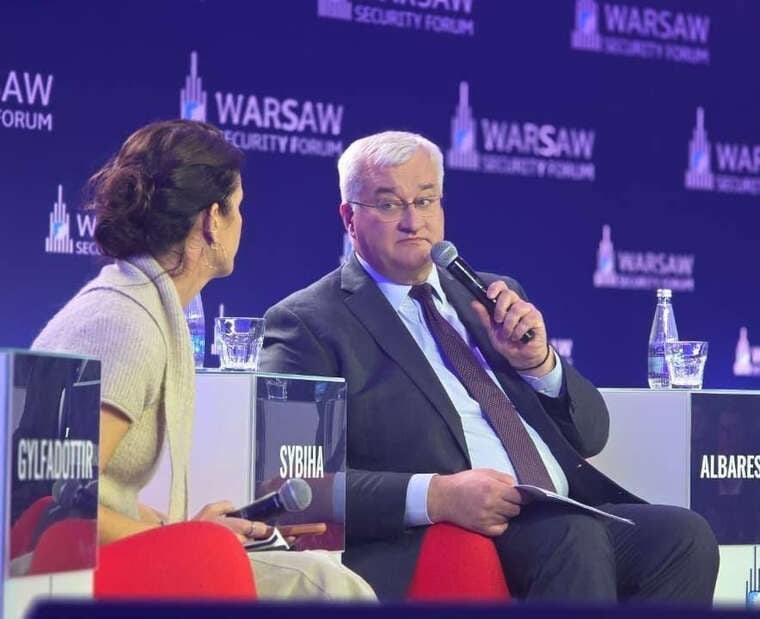
Foreign Minister Andrii Sibiha stated that in less than two years, Kyiv's position on the international stage has shifted from a lack of leverage to the ability to demand that partners refrain from using their cards.
BAMF has begun more actively revoking protection statuses for Syrian citizens, citing the change in the political situation in the country, although this does not imply automatic deportation.
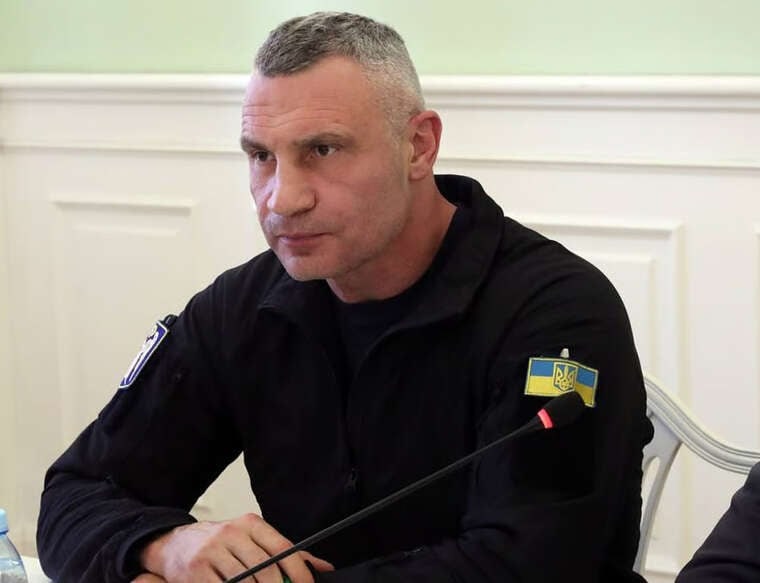
Kyiv Mayor Vitali Klitschko has been summoned to parliament. The reasons for the summons and the date of his appearance are not specified in the available information.
Apps with offline maps seem like a convenient solution, especially when you need to use a navigator without internet access. However, behind the attractive offer, which is often advertised on social media, a serious threat may be hidden. Criminals are spreading malicious software that gives them access to victims' personal data and bank accounts.
Criminals post ads for a navigator that allegedly works without the internet, contains no ads, and is completely free. After clicking the link, the user lands on a third-party resource where they are offered to download a file via a Telegram bot.
Instead of the promised useful program, the person receives a malicious file. During installation, the system may request permission to install apps from unknown sources, as well as access to various smartphone functions. If the user agrees, criminals gain the ability to monitor actions on the device, intercept messages, and steal confidential information.
Particularly dangerous is the malware gaining access to SMS, notifications, or functions that allow controlling the gadget's operation. This gives scammers the opportunity to seize login credentials and gain access to financial services.
To avoid losing data and funds, follow these rules:
If there are grounds to believe that the smartphone is infected, it is necessary to immediately stop using banking apps and other critical services on it. If possible, the device should be disconnected from the internet, and another, safe gadget should be used to change passwords for important accounts.
After that, the suspicious app needs to be deleted, and the permissions it was granted should be checked. If the program cannot be deleted or continues to run, it is worth seeking technical assistance. If you entered banking details or noticed suspicious transactions, you must immediately contact the bank and request account protection.
Facts of fraud should be reported to the Cyber Police via the official online form. Additional information about current fraud schemes and protection methods can be found on the StopFraud platform.
It is important to remember: even a seemingly useful app can become a tool in the hands of scammers. Smartphone security depends on the user's reasoned decisions: do not rush to download, verify the source, and do not grant apps unnecessary permissions.
Comments
No comments yet. Be the first!